The wp-config.php file is usually found in the main WordPress installation folder, often public_html, the site’s domain folder, or one level above the web root for extra protection. It is the file that stores database connection details, security keys, table prefix settings, and other site-level configuration rules. WordPress confirms that this file is one of the core configuration files used during installation and runtime [source: WordPress Developer Resources].
TLDR: In most cases, wp-config.php sits beside folders such as wp-admin, wp-content, and wp-includes. For example, a site installed at example.com may store it at /public_html/wp-config.php, while an addon domain may use /public_html/example.com/wp-config.php. A support technician checking 20 WordPress sites may find about 80% of them in the domain root, 15% in subfolders, and 5% one level above the web root. cPanel is usually the fastest tool for finding it, while the WordPress dashboard normally cannot show or edit it directly.
Why wp-config.php matters
The wp-config.php file controls settings that WordPress needs before the dashboard even loads. If the database name, username, password, or host is wrong, the site may show the classic “Error establishing a database connection” message.
That is why this file gets so much attention during migrations, repairs, staging setup, malware cleanup, and SSL fixes. One small typo can break the whole site. It drives many site owners crazy because the file looks simple, yet one misplaced quote can cause a blank screen.
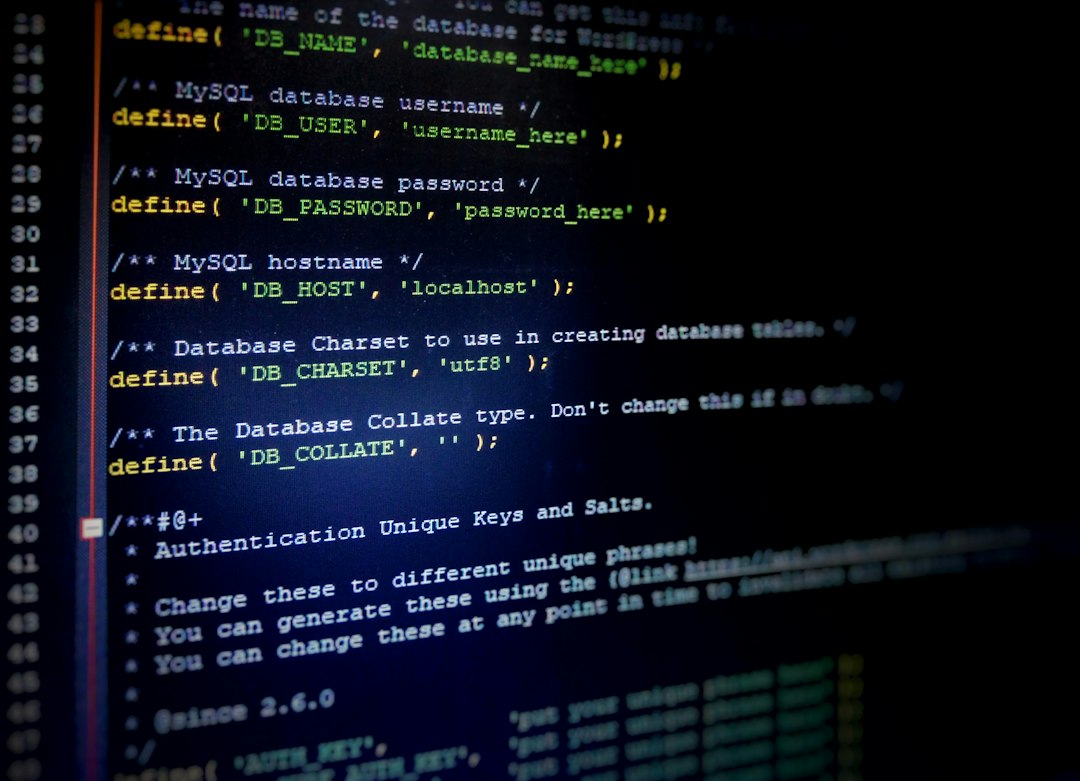
Common values inside wp-config.php include:
- DB_NAME: the database name used by WordPress
- DB_USER: the database username
- DB_PASSWORD: the database password
- DB_HOST: often
localhost, but not always - AUTH_KEY and salts: security values for logins and cookies
- $table_prefix: the prefix before WordPress database tables
- WP_DEBUG: a setting used for error troubleshooting
Where WordPress places wp-config.php
A standard WordPress install places wp-config.php in the same folder as wp-admin, wp-content, and wp-includes. This folder is often called the WordPress root directory.
Typical locations include:
/public_html/wp-config.phpfor the main domain/public_html/blog/wp-config.phpfor a site installed in a blog subfolder/public_html/domain.com/wp-config.phpfor an addon domain/home/accountname/wp-config.phpif the host has moved it one level abovepublic_html
The last location surprises people. WordPress can read wp-config.php from one directory above the WordPress root in many standard setups. Some administrators use that placement to reduce public exposure. It is not magic. It is just a supported file lookup behavior.
Can the WordPress dashboard find it?
Not usually. The WordPress admin area does not provide a normal screen for opening wp-config.php. That is intentional. The file contains sensitive database credentials, so showing it inside the dashboard would be risky.
Some file manager plugins can display server files from inside WordPress. That sounds handy, but it can be a bad idea on production sites. If an admin account gets hacked, the attacker may gain access to the configuration file. Honestly, it feels like saving 30 seconds in exchange for a much larger cleanup bill later.
The WordPress dashboard can help indirectly, though. It can show clues such as the site URL, active plugins, theme path, and media upload location. Those clues may help a developer guess whether WordPress is installed in the root folder, a subfolder, or an addon domain directory.
How cPanel makes the file easier to find
cPanel is usually the better tool for locating wp-config.php. Its File Manager shows the hosting account’s folder structure, including public_html, addon domain folders, backups, logs, and sometimes staging directories.
A typical cPanel process looks like this:
- Open cPanel.
- Go to File Manager.
- Open
public_html. - Look for
wp-admin,wp-content, andwp-includes. - Check the same folder for
wp-config.php. - If it is missing, check one folder level above.
For addon domains, cPanel may store each site in its own folder. A domain called example.net might live in /public_html/example.net/ or in a custom folder such as /domains/example.net/. Hosts love changing these defaults, which adds needless searching.
WordPress vs cPanel: key differences
The main difference is access level. WordPress is an application. cPanel is a hosting control panel. WordPress runs after the server reads configuration files. cPanel works at the file-system level, before WordPress needs to function.
| Method | Can locate wp-config.php? | Best for |
|---|---|---|
| WordPress dashboard | Usually no | Checking site settings and plugin clues |
| cPanel File Manager | Yes | Opening folders and editing files |
| FTP or SFTP | Yes | Developer access and safer file transfer |
| SSH | Yes | Fast search commands and advanced repair |
For most non-technical site owners, cPanel File Manager is the clearest option. For developers, SFTP or SSH is often cleaner and safer. A simple SSH command such as find ~/ -name wp-config.php can locate every matching file in the hosting account, although shared hosts may restrict that access.
What if wp-config.php is not in public_html?
If the file is not in public_html, the site owner should check three places. First, the domain’s actual document root. cPanel often shows this under Domains. Second, one level above the WordPress folder. Third, a staging or managed WordPress directory created by the host.
Some managed hosts hide direct file access or use custom folder structures. In those cases, the host’s file browser, SFTP credentials, or support team may be required. Expect to waste time on naming habits such as wordpress, site, htdocs, or www. None of them is universal.
Safe editing tips
Before editing wp-config.php, a backup should be created. The file is small, but it is critical. A plain copy named wp-config-backup.php can help, although it should not stay publicly accessible for long.
- Download a copy first before making changes.
- Use plain text editing, not a word processor.
- Do not remove quotes around database values.
- Check file permissions, often
400,440, or600depending on the host. - Avoid editing from unknown plugins inside WordPress.
FAQ
Where is wp-config.php usually located?
It is usually in the WordPress root folder, beside wp-admin, wp-content, and wp-includes. On many cPanel accounts, that means /public_html/wp-config.php.
Can wp-config.php be outside public_html?
Yes. It may sit one folder above public_html or above the WordPress install folder. Some site owners do this for added protection.
Can the WordPress dashboard open wp-config.php?
Not by default. WordPress does not include a built-in editor for this file. File manager plugins may access it, but that can increase security risk.
Is cPanel the best way to find wp-config.php?
For many hosting accounts, yes. cPanel File Manager gives direct access to folders, domain roots, and addon domain directories.
What happens if wp-config.php is deleted?
WordPress will stop connecting to the database. The site may show an installation screen or a database connection error. Restoring the file from backup is the safest fix.
Should wp-config.php be edited often?
No. It should only be edited for clear tasks such as database changes, debugging, security keys, memory limits, or migration fixes.